
Every change validated before it reaches production.
Code Guardian reviews every branch or pull request against what was requested in Jira, your team’s rules and quality and security analysis. It comments on the affected lines and can prevent the merge.
- Coverage against the Jira ticket
- Your team’s rules (playbook)
- SonarQube and Semgrep
- Merge blocking
- Jira ticket covered
- Team rules enforced
- Vulnerabilities reviewed
Manual reviews do not scale and risks slip through.
Code Guardian adds an always-on review that compares what was done with what was requested and with the team’s rules, and explains it in the pull request itself.
Inconsistent reviews
Each reviewer looks at different things and big changes get approved out of fatigue.
Something different is implemented
The pull request does not cover what the ticket said and nobody notices until late.
Separate tools
Quality, security and team rules are checked in different places.
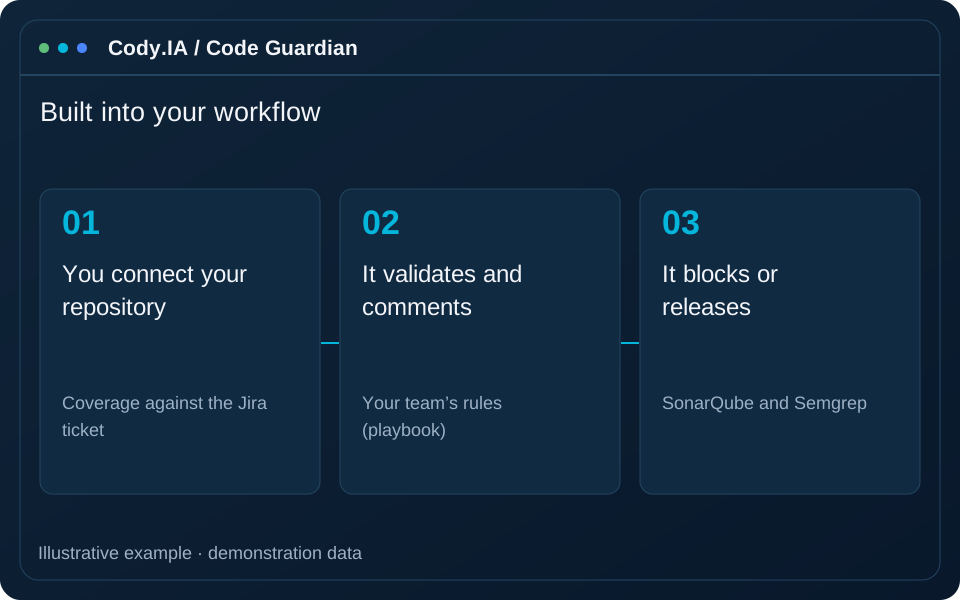
Built into your workflow
-
1
You connect your repository
With a GitHub webhook or a GitHub Actions workflow generated with one click.
-
2
It triggers on every PR
The Jira ticket is found from the branch or PR name and the validations run.
-
3
It validates and comments
It compares against the ticket, your rules playbook, SonarQube and Semgrep, and comments on the affected lines.
-
4
It blocks or releases
With one button you configure changes with findings so they cannot be merged until fixed.
Blocking depends on configured thresholds and the repository requiring the check. Connected tools complement human review and team tests.
A review that never tires
Coverage against Jira
Checks that the change really covers what the ticket asked for.
Rules playbook
Applies your team’s rules and standards on every review.
SonarQube and Semgrep
Code quality and vulnerability scanning in the same validation.
Inline comments
Findings appear on the exact line of the pull request, with their explanation.
Merge blocking
Set the check as a branch requirement to stop what does not comply.
Automatic trigger
By GitHub webhook or by GitHub Actions with its own key.
Who uses it
Instant feedback
Receive observations tied to the change and ticket context so issues can be addressed before another review. Comments guide the PR discussion and let the team focus its time on design and behaviour decisions.
Consistency
Define technical and style rules in a playbook and choose which severities should fail the check. Functional, technical, vulnerability and style groups organize review around your team criteria and integrations.
Control without friction
Bring findings from configured tools into the regular review workflow. Prioritize by severity and context, verify reported cases and require the agreed checks in branch protection before allowing a merge.
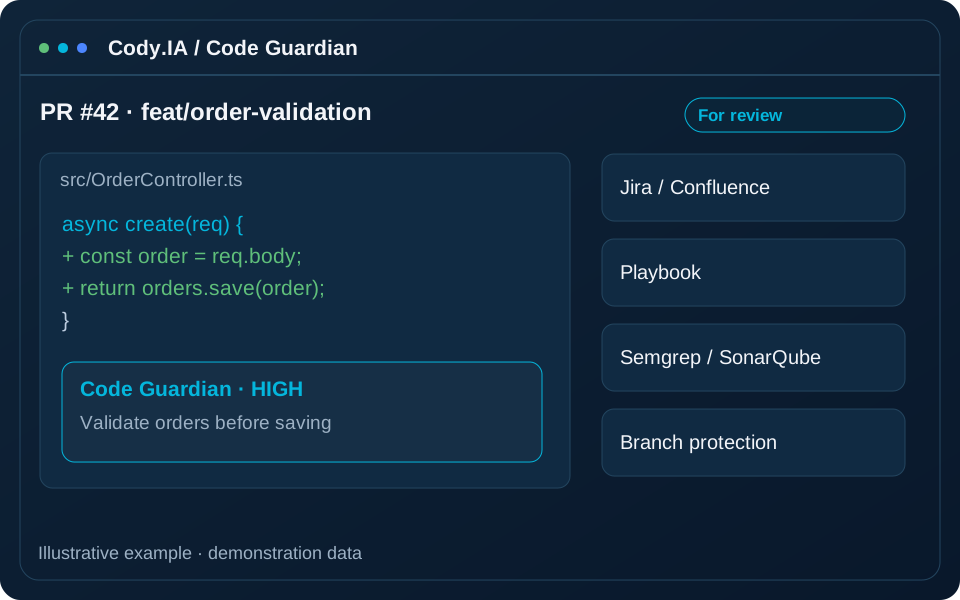
Plugs into your workflow
Security in the tool itself
Signed webhooks
GitHub events are verified with a cryptographic signature.
Protected keys
GitHub Actions keys are stored hashed, never in clear text.
Protections respected
When requiring the check, the protections the branch already had are preserved.
Frequently asked questions
Put a guard on every pull request
We connect it to one of your repositories and you see what it finds in a real change.