
Your entire cloud, mapped and explained.
You connect your account, Cloud Infrastructure discovers every resource, and the AI turns them into diagrams, security and cost analysis, and even infrastructure code ready to review.
- AWS, Google Cloud and Azure
- Architecture diagrams
- Security and costs
- Terraform and CloudFormation
Nobody has the real map of what is in the cloud.
Cloud Infrastructure inventories what actually exists and analyzes it: what relates to what, what it costs, which risks exist and how it would look as code.
Orphan resources
Over time machines, disks and services pile up that nobody uses and you still pay for.
Invisible risks
Insecure configurations and exposed secrets go unnoticed among hundreds of resources.
Infrastructure without code
What was created by hand in the console is hard to reproduce, audit or migrate.
From a credential to a complete map
-
1
You connect your cloud
Enter your AWS, Google Cloud or Azure credentials. They are encrypted and used only for that request.
-
2
Resources are discovered
The platform walks your account and skips, without failing, the categories where you lack permissions.
-
3
The AI analyzes
It generates diagrams, security posture, costs, network topology, dependencies and tag governance.
-
4
You export and act
Get Terraform or CloudFormation code and detect changes against a previous discovery.
From inventory to decisions
Multi-cloud discovery
AWS, Google Cloud and Azure from a single place, with automatic pagination and minimal permissions.
Diagrams and topology
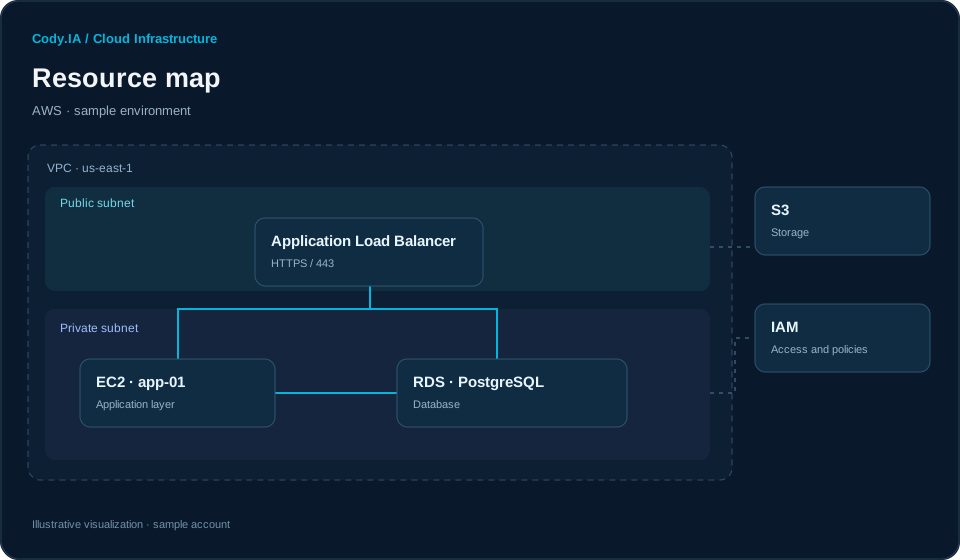
Architecture, network and dependencies drawn automatically, with impact analysis.
Security posture
Security and compliance assessment, and detection of exposed secrets.
Costs and savings
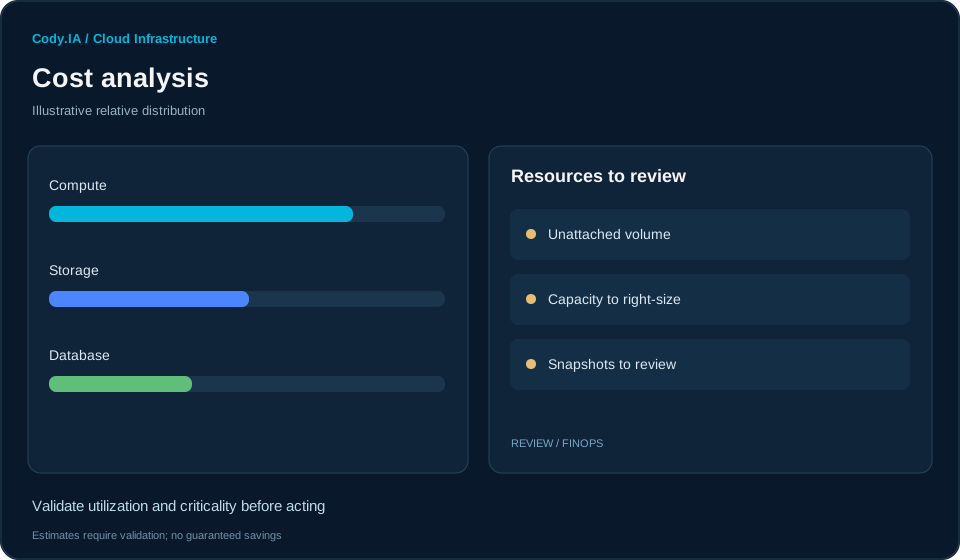
Costs by category, unused resources and right-sizing recommendations; on Azure, with real public prices for virtual machines.
Infrastructure as code
Generate Terraform or CloudFormation; on Azure, from Microsoft’s real API so no attributes are invented.
Drift and tags
Detect changes between discoveries and check tag governance.
Who it is for
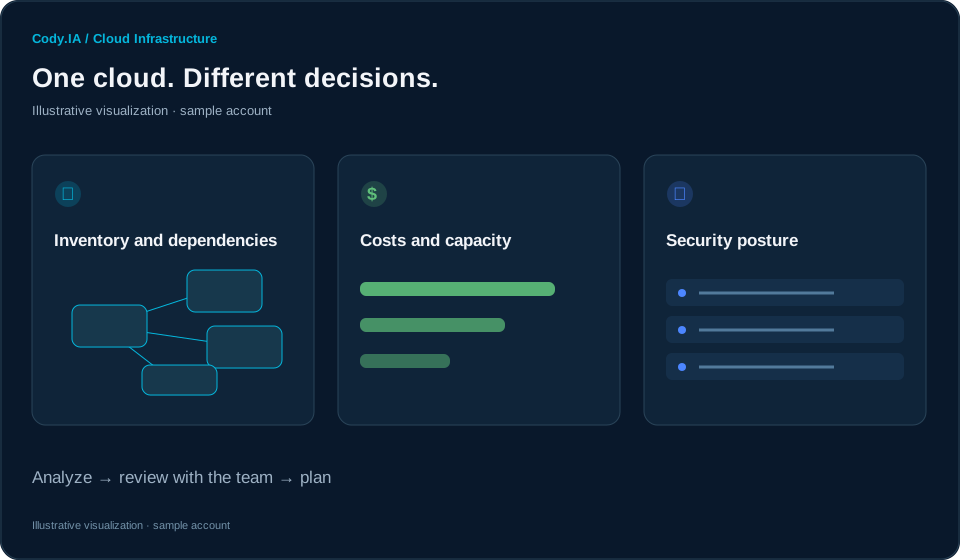
Make decisions with a map, not assumptions.
See compute, networking, storage and databases in one view. Review relationships and dependencies before planning changes, investigate differences between discovery runs and use the inventory to discuss architecture and maintenance with your team. Generated Terraform or CloudFormation is a starting point for review; changes are evaluated and applied through your organization’s processes.
Understand spending before optimizing.
Review cost distribution across categories and identify resources worth a closer look: unattached disks, apparently idle services or capacity that may be right-sized. Compare recommendations with utilization, billing and continuity requirements. Figures may be estimates; public prices are used where available. An optimization opportunity is not confirmed savings or authorization to delete resources.
Turn findings into review priorities.
Connect inventory with configurations and dependencies to guide review of exposure, access and security posture. Share findings with infrastructure and application owners to validate scope and agree on actions. Analysis supports your team and depends on available permissions and data; it does not replace an audit, security testing or compliance validation.
The clouds you already use
Credentials handled with care
Credentials per request
They are used only for that request and are not kept in global server variables.
Encrypted at rest
Credentials you choose to save are stored encrypted.
Read-only on databases
Schema inspection runs in read-only mode, enforced in three layers.
Frequently asked questions
You may also like
See your cloud with fresh eyes
Let us connect a test account and show you the map, the costs and the risks that come up.